Cyber Security
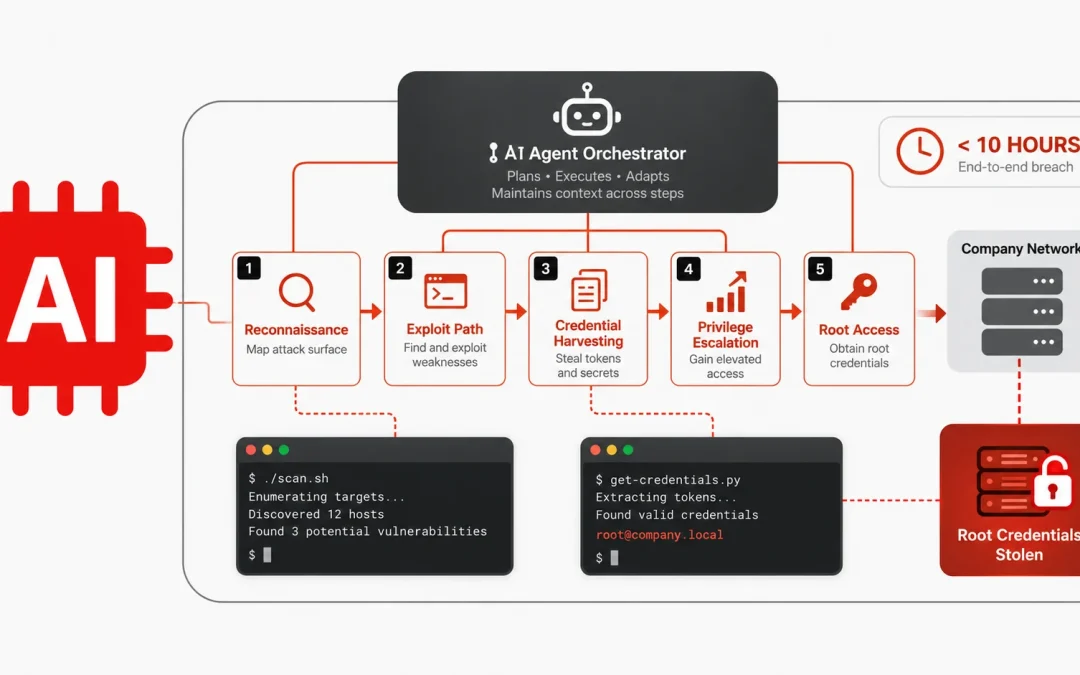
A human attacker armed with frontier artificial intelligence models breached an enterprise network and seized root credentials in under 10 hours, a timeline that would normally take human red teams roughly two weeks to complete, according to a new incident response...
Cyber Security
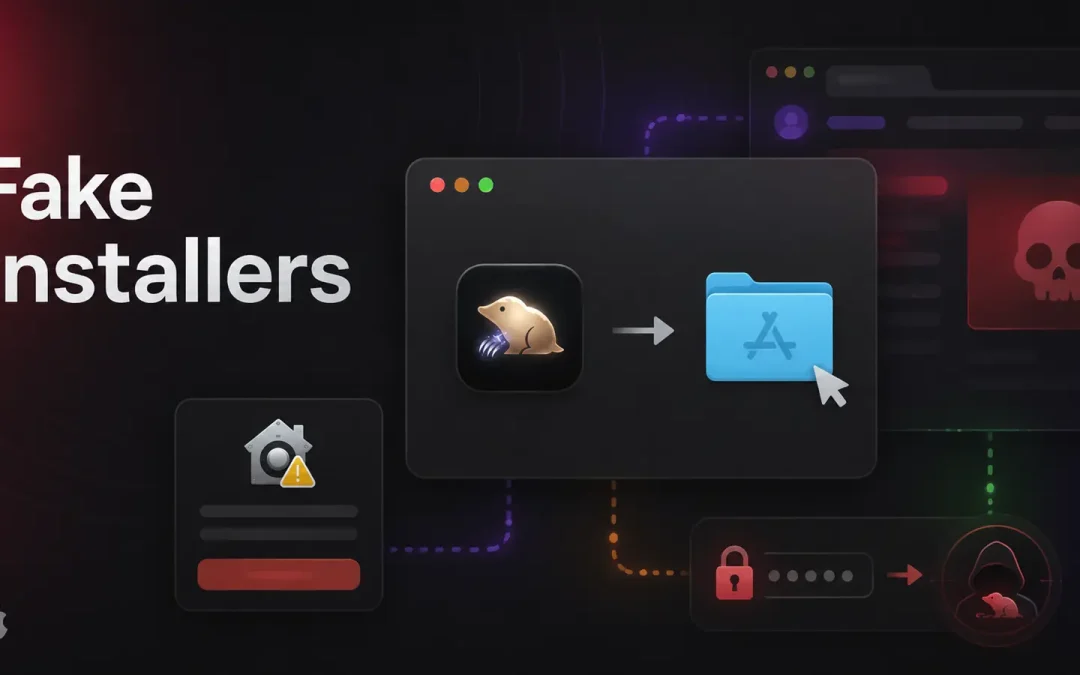
Mac users are being targeted with 14 fake application installers that appear to offer familiar software but instead start a credential-stealing remote-access trojan. The files were distributed as macOS disk images and installer packages, giving attackers another route...
Cyber Security
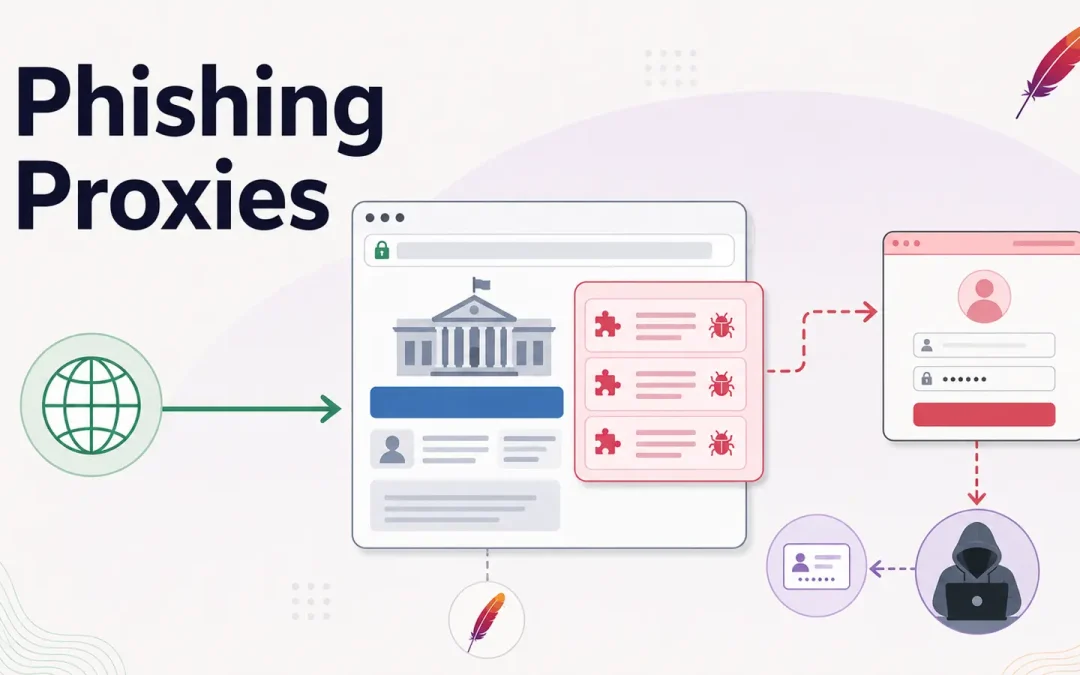
Brazilian government websites have been quietly turned into gateways for phishing pages on trusted public domains. Rather than sending victims to obvious scam sites, attackers are using compromised web servers to make fraudulent content look legitimate immediately....
Cyber Security
HPE has released security updates for HPE Networking Fabric Composer following the discovery of a large set of vulnerabilities that could allow unauthenticated attackers to gain administrator access, run arbitrary commands, and fully compromise affected systems. The...
Cyber Security
Hackers are using booby-trapped website themes to turn visits from iPhone users into a route for spyware and cryptocurrency theft. The campaign hides harmful code inside themes used by Vietnamese movie and comic streaming websites, exposing visitors without warning....
Cyber Security
A newly disclosed security flaw in Composer, the widely used dependency manager for PHP, could allow a malicious or compromised package to alter permissions on files located outside its own installation directory. The issue, tracked as CVE-2026-59944, can expose...
Cyber Security
OpenAI is pulling its AI models from Cursor following SpaceX’s acquisition of the AI coding assistant, notifying SpaceX that it will wind down the contract that supplies those models to the editor. The proposed shutoff date is November 12, 2026, which OpenAI said is...
Cyber Security
Malvertising is becoming harder to identify by looking at the ad itself. A growing share of malicious advertising activity now depends on what happens after the click: redirect chains, disposable domains, cloaking systems, conditional delivery, and campaign behavior...
Cyber Security
Dark Caracal has returned with a new tool that helps attackers stay connected when defenders shut down their control servers. The cyberespionage group is linked by researchers to a Venezuelan communications organization intrusion, where it deployed an unfamiliar...
Cyber Security
SLEEPWALKER is a Windows backdoor built to stay quiet until an operator sends a specially crafted network packet. Rather than calling home to a fixed command server, it hides inside a trusted management process and waits, creating little network activity for defenders...