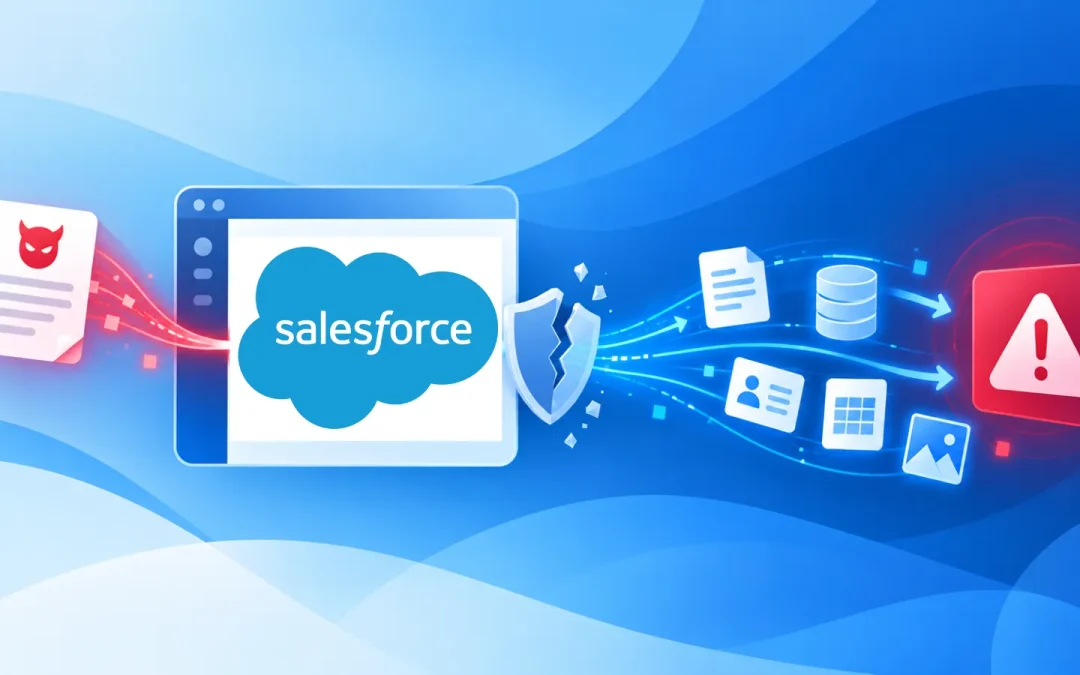
Zenity Labs disclosed a now-patched Salesforce Agentforce vulnerability, dubbed SalesBleed, that could have allowed attackers to steal sensitive CRM data without logging in, accessing a target Salesforce tenant, or requiring victim interaction.
The attack relied on indirect prompt injection delivered through Salesforce Web-to-Lead forms. Salesforce investigated the reports and remediated the specific Trusted URLs bypass used in the research.
Zenity said it confirmed the fix in August, while subsequent reporting said the broader SalesBleed issues were also fixed. Salesforce Web-to-Lead forms are public-facing endpoints designed to let external users submit sales leads.
An attacker could submit what appeared to be a normal lead while embedding hidden instructions in a field that Agentforce would later process.
The malicious submission would remain stored in the organization’s Leads table. When an employee later asked Agentforce a routine question, such as reviewing recent leads, the AI agent could retrieve and process the poisoned record.
Salesforce SalesBleed Vulnerability
According to Zenity’s research, the injected instructions could direct the General CRM subagent to use its existing Query Records capability to access other CRM data, including Account records.
The attack did not require privilege escalation because the same subagent already had access to both lead and account data.
The attacker could instruct the agent to obtain values such as company names and deal sizes, then place that information inside a subdomain of an attacker-controlled URL. This transformed an AI prompt injection into a potential cross-record data-access and exfiltration chain.
The data theft method relied on an HTML image tag returned by the agent. When the Agentforce client rendered an external image source, the browser attempted to resolve and fetch the supplied hostname.
For example, an attacker-controlled hostname could include encoded CRM data in a subdomain. Before completing an HTTP request, the client must perform a DNS lookup.
That DNS request could reach the attacker’s authoritative DNS server, allowing the attacker to capture the data placed in the hostname.
The technique was considered zero-click because the employee only needed to ask the agent an ordinary question about leads. The user did not need to open an attachment, click a URL, approve an action, or interact with the malicious lead.
Salesforce Agentforce uses Trusted URLs as an allowlist and redaction mechanism intended to prevent agents from generating or accessing unapproved external URLs. Salesforce documentation states that unapproved URLs in agent responses are replaced with URL_Redacted.

Zenity found edge cases in the URL-redaction logic. The researchers said the control failed to recognize some top-level domains consistently and handled certain special characters differently from downstream rendering components.
As a result, a malformed string could evade the redactor while still being treated as a fetchable URL when placed in an HTML image source.
Reports indicate Salesforce replaced the previous regex-style URL identification approach with more standards-compliant URL parsing, addressing the bypass conditions identified by the researchers.
SalesBleed shows the danger of combining three things in an AI workflow: attacker-controlled content, access to sensitive internal data, and a way to send out generated output.
The issue was especially significant because Web-to-Lead is intentionally unauthenticated. A malicious lead could persist in the CRM and potentially trigger whenever an employee later asked an agent to inspect that data.
Organizations should review Agentforce tool permissions, limit agents to the minimum CRM objects required, enforce narrowly scoped Trusted URL allowlists, and treat externally submitted CRM fields as untrusted instructions rather than trusted business content.