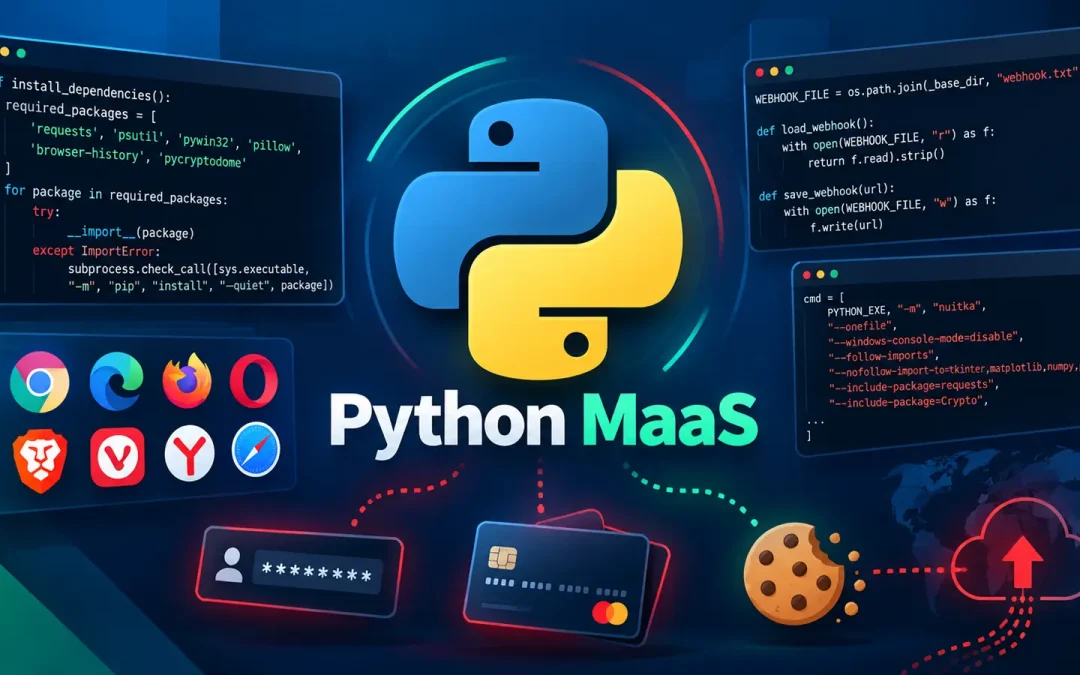
A Python-based malware builder can turn a single stealer into Windows programs for different operators. The tool packages a payload designed to take saved passwords, payment card details and browser cookies, then send them to an attacker-controlled webhook set by its operator.
Its reach extends beyond browsers to messaging accounts, wireless passwords and details about the infected computer. The sample reached researchers inside a compressed archive containing another archive with the builder.
This shows its packaging, but the report does not establish how victims receive it or how many machines were infected.
Its builder-and-payload design resembles other malware-as-a-service credential theft operations that let users produce separate builds. Analysts at K7 Security Labs identified the two-part tool while examining the nested package.
The immediate risk is not limited to exposed passwords. Stolen session cookies may let an intruder use an account that is already signed in, even without knowing its password, while payment details and wireless passwords widen the damage. As infostealer logs fuel compromises, one infected machine can affect more than its owner.
Python MaaS Infostealer Builder
The payload checks user data folders for 17 Chromium-based browsers and reads saved login details, browsing history, payment card entries and session cookies.
It copies browser databases to a temporary location when locked, then uses Windows data-protection functions and browser encryption keys to recover stored secrets. This is a Windows threat, not a browser exploit.
Firefox is also in scope, but separately from those 17 browsers. The stealer reads Firefox history and cookie records, while Chromium routines also target passwords and cards.
Similar breadth appears in other browser-focused stealer investigations, but the number 17 in this case refers specifically to Chromium-based browsers. The malware searches for Discord tokens, checks whether they still work and collects Roblox session cookies.

These items can be valuable because an active session may offer access without requiring a fresh password. It searches saved Wi-Fi profiles for their passwords too, adding network credentials to the stolen browser and account data.
Location and system details round out the collection. The payload records the victim’s public IP address, approximate location, time zone, Windows user name and computer name.
It then builds an archive in memory and sends it through a configured webhook. This leaves less file-system evidence than writing an archive to disk before upload.
Builder Evasion and Detection
The builder installs missing Python dependencies automatically and stores its chosen webhook for later build sessions.
It encodes that address using XOR and Base64 before insertion into the payload, so a simple search for the plain address in a compiled program may fail. Operators can choose between two executable-building methods or keep a raw script for changes.
Once launched, the stealer tries to avoid examination. It checks for a debugger, looks for signs of virtual machines, exits on systems with less than 50 GB of disk space and varies its sleep time.
It also delays loading some libraries until they are needed. These checks may hinder short automated tests without changing what it steals.
To return after a restart, the payload uses both a Windows startup registry entry and a scheduled task that runs at logon. This gives it another chance if one is removed.

Like Python stealer targeting Discord, it also treats account tokens as data worth checking before sending to the operator.
K7 recommends watching for unusual Python package installation, unexpected startup entries or scheduled tasks, access to browser credential stores and outbound posts to unfamiliar webhooks.
Users should double-check downloaded files before opening them and keep security protections current. Defenders should judge these behaviors together rather than rely on hashes, since individual builds can vary when operators change their settings for each build.
Indicators of compromise (IoCs):-
| Type | Indicator | Description |
|---|---|---|
| SHA-256 | 1ab7846f93678fb727c95df133c1b0a050760b11dd164ca5f6408e84398b676e |
Archive examined by the researchers, identified through a VirusTotal link. |
| SHA-256 | 7053dc55b4ba193ea162f01a329427fd244d8163a65cbf2a7f86c04c849c8114 |
Nested builder archive identified through a VirusTotal link. |
| SHA-256 | 9e471343255259f7fb388f1f07b0e023261630dbdc01f5d647dc99f452119eff |
Python stealer sample identified through a VirusTotal link. |
| MD5 | 610f0c65a3f8e88559f89ed90ea9ee5c |
Listed as Password-Stealer ( 006dba241 ). |
| MD5 | 429ed63ab3fbda8d22d0ac750ecfe8cc |
Listed as Password-Stealer ( 006dba241 ). |
| MD5 | 9ffe0e45c7a3f20e4481206c1c3b0854 |
Listed as Trojan ( 006e632e1 ). |
| File name | my new program called 2.rar |
Outer archive examined by the researchers. |
| File name | TokenGrabberBuilder.zip |
Nested archive containing the builder. |
| Folder name | TokenGrabber Builder |
Folder inside the nested archive. |
| File name | stealer.py |
Python stealer script. |
| File name | webhook.txt |
Builder file used to retain a configured webhook address. |
| Archive name pattern | StolenData_ |
Name assigned to the stolen-data archive assembled in memory. |
| Registry value | HKCU\Software\Microsoft\Windows\CurrentVersion\Run\WindowsUpdate |
Autorun location and deceptive value name used for persistence. |
| URL | https://pastebin.com/api/api_post.php |
Legitimate service API address shown in the malware’s decoded strings as a secondary exfiltration endpoint; not a unique attacker-controlled URL. |
| Target file | Local State |
Chromium browser file accessed for encryption-key material. |
| Target file | Login Data |
Chromium database targeted for saved logins. |
| Target file | History |
Chromium database targeted for browsing history. |
| Target file | Web Data |
Chromium database targeted for payment card details. |
| Target file | Cookies |
Chromium cookie database targeted for sessions. |
| Target file | Network/Cookies |
Alternate Chromium cookie database location. |
| Target file | places.sqlite |
Firefox history database targeted by the stealer. |
| Target file | cookies.sqlite |
Firefox cookie database targeted by the stealer. |
| Process name | pip.exe |
Unexpected execution by a non-development application is a behavioral clue, not evidence of infection on its own. |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.