
Insights
Security and compliance insights
Practical guides, explainers and regulatory updates on compliance frameworks, security testing and AI risk, written by the CyberAccord Security Team.
Latest · Explainer
SOC 2 Type I vs Type II: which report do you need?
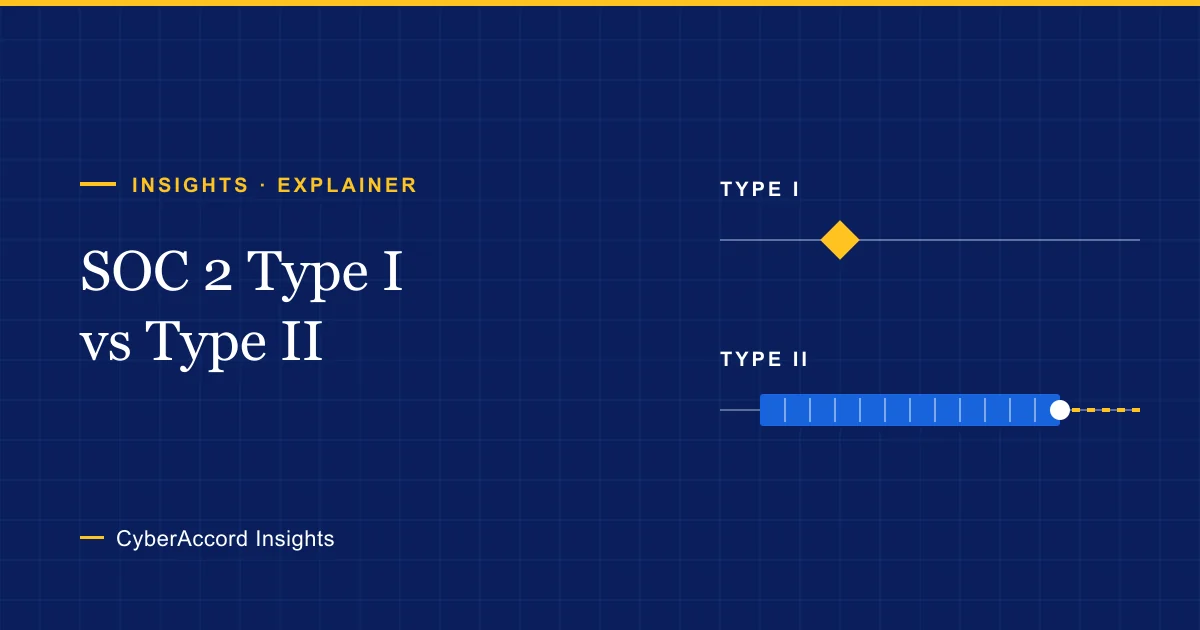
Both reports are issued by an independent CPA firm against the same AICPA criteria. The difference is time: one date versus a period of evidence.
By CyberAccord Security TeamPublished 6 min read
Key takeaways
- A Type I report covers control design at a point in time; a Type II report adds testing of operating effectiveness over a period.
- Only a licensed CPA firm can issue a SOC 2 report, under the AICPA attestation standards and SOC 2 guide.
- A Type I makes sense for a first report or a near-term customer deadline; plan the Type II period to start soon after.
- Buyers read the period dates, scope, exceptions, user entity responsibilities and subservice organizations, not just the opinion.
- A bridge letter covers the gap between the end of the last report period and today; it is not a new audit opinion.
Guides
 Guide
What does the FTC Safeguards Rule require of small firms?
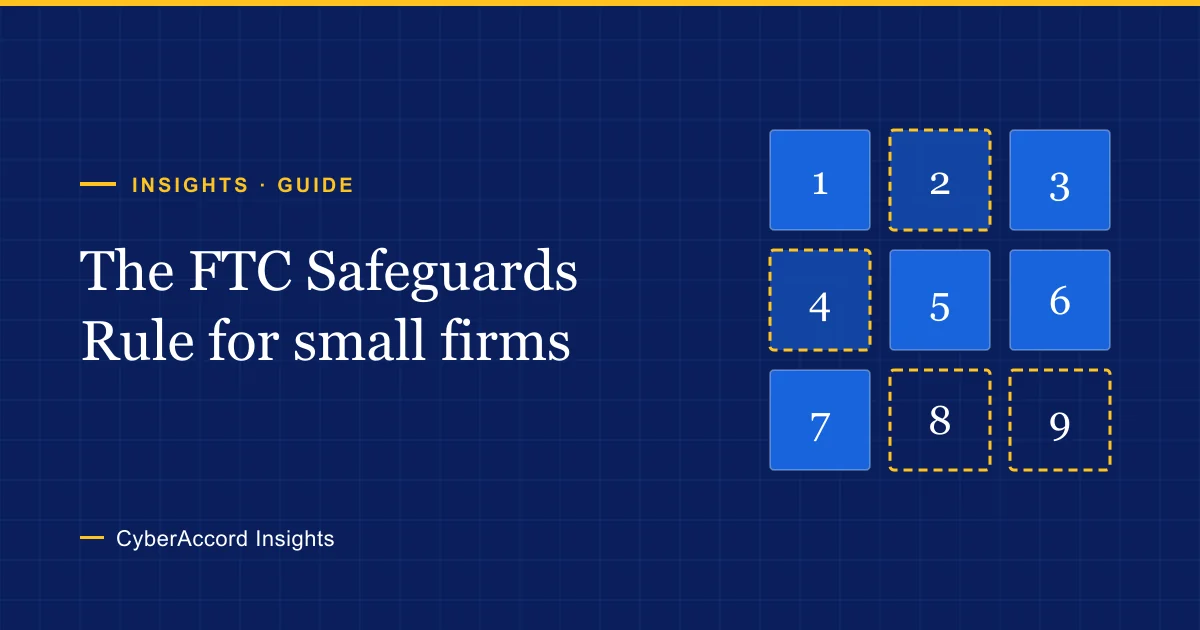
Who the FTC Safeguards Rule covers, its nine required elements, what the under-5,000-consumer exemption removes, and the 30-day FTC breach notice.7 min read Guide
How do you answer customer security questionnaires well?
How to answer SIG, CAIQ, HECVAT, and custom security questionnaires accurately: an answer library, the right evidence, honest gaps, and clear ownership.6 min read Guide
What does ABA Model Rule 1.6(c) require of a law firm's security?
How Model Rule 1.6(c), the Comment [18] factors and ABA Formal Opinions 477R, 483, 498 and 512 translate into a law firm security program.7 min read
Stay current
Follow CyberAccord on LinkedIn
We post new articles and regulatory changes there as they are published.
Prefer a feed reader? Subscribe to the RSS feed.
Talk to a security practitioner
Book a free 20-minute consultation. We'll learn what's driving the need and recommend a scoped next step with a fixed quote.